Checking that audit records are unaltered
Audit records are hash-chained: each one carries a fingerprint of the record before it, so changing or deleting any record breaks every fingerprint after it. Both tabs of Audit Logs show you where that guarantee holds, and Access & sign-in lets you test its whole chain.
- The Audit Logs app in your top bar.
- These permissions: Audit Log · Events - Read, Audit Log · Integrity - Execute.
- Verify Integrity runs with either of these permissions.
If Audit Logs isn't in your top bar, your role can't view it or your plan doesn't include it. Ask a workspace administrator, or see Permissions and module visibility.
Steps
Open Audit Logs
Select the Audit Logs icon in the top bar, the red scroll. It opens on Documents & configuration.
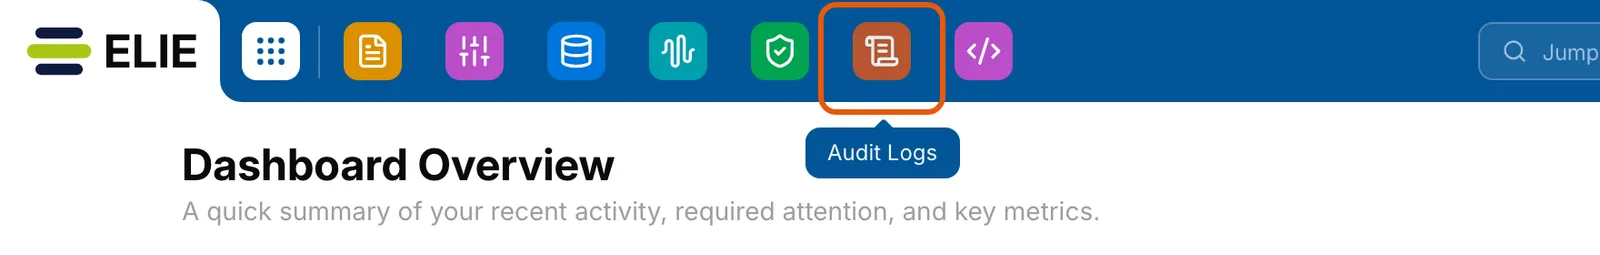
The top bar of Elie with the module icons. The red scroll icon, the last one, is ringed and its tooltip reads Audit Logs. EnlargeLook for flagged rows
Under the list, a line reads _Every row here is hash-chained and provably unaltered, unless flagged in the list._ A row outside the chain shows Not chained after its sentence; point at it for the reason.
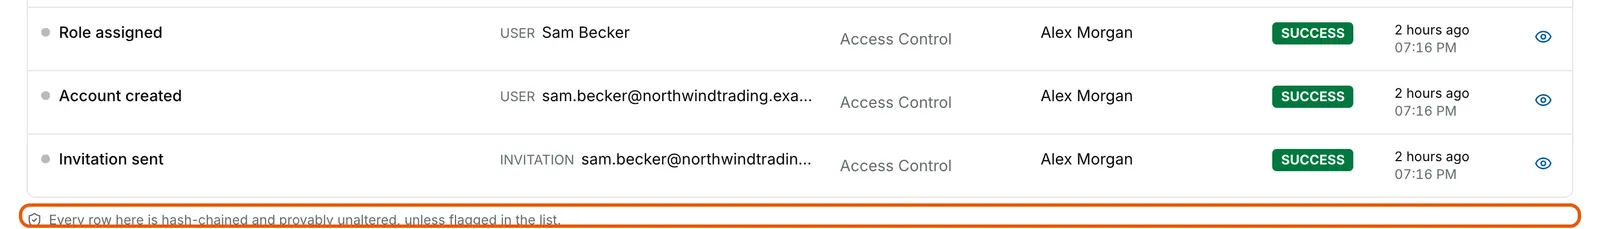
The last rows of the timeline, none flagged, and under them the ringed footnote Every row here is hash-chained and provably unaltered, unless flagged in the list. EnlargeCheck one row
Select Show details on the row. Its panel ends with Hash-chained and unaltered, or with a red line saying the row is not covered by the hash chain.
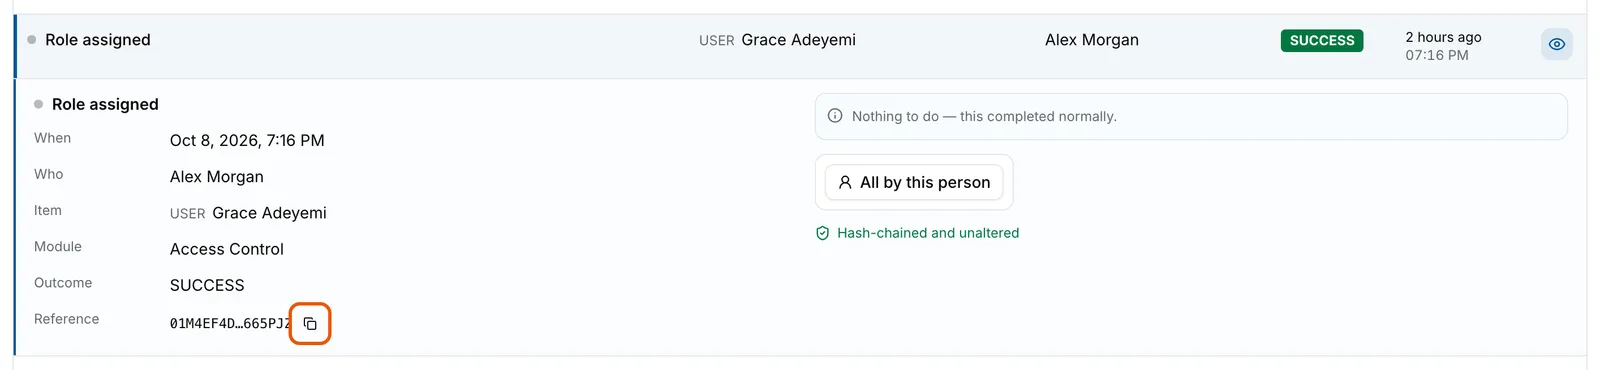
A Role assigned row opened in place, ending in the green line Hash-chained and unaltered under its advice and All by this person. EnlargeVerify the sign-in chain
Select Access & sign-in, then Verify Integrity under the list. It reads Verifying… while it walks the security service's record from its first event.
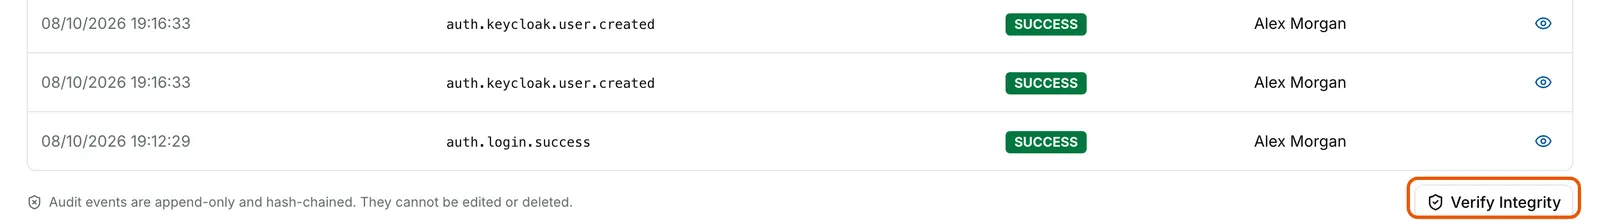
The bottom of the Access & sign-in list: the last rows, then the line Audit events are append-only and hash-chained, they cannot be edited or deleted, beside the ringed Verify Integrity button. EnlargeRead the result
A banner above the list reports it: green with the number of events verified, or red with the event and sequence number where the chain broke. Close it with its cross.
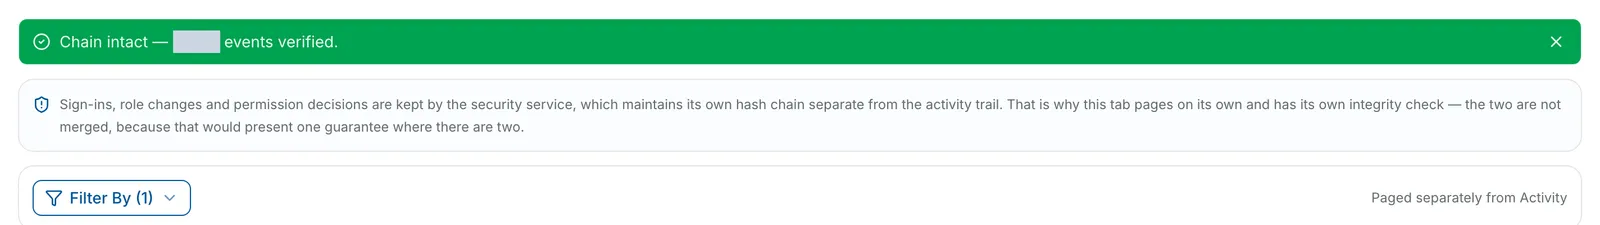
The green banner Chain intact, with the number of events verified, at the top of the Access & sign-in tab above the note about the separate chain and the Filter By toolbar. The number is masked because it grows with every event. Enlarge


What success looks like
- No row on Documents & configuration shows Not chained.
- The Verify Integrity banner is green and counts the events it checked.
- In a CSV from Export this page, the Verified column reads
trueon every row.
What the chain does and does not prove
A chained record has not been altered since it was written. It says nothing about whether the action itself succeeded; failures are recorded and chained like everything else. The two tabs are separate chains, which is why each has its own check: Documents & configuration marks each row, and Access & sign-in offers the whole-chain test. There is no button to test the activity chain yourself.
If something goes wrong
| Symptom | Likely cause | What to do |
|---|---|---|
| A row shows Not chained. | That record is outside the hash chain, so it cannot be proven unaltered. | Open it, copy its Reference and send it to support. |
| The banner is red and names an event and sequence number. | A record in the sign-in and access chain no longer matches its fingerprint. | Note what the banner says and contact support. |
| Integrity check could not be completed. | The check could not run just now. | Try again later. |
| Verify Integrity is nowhere on screen. | You are on Documents & configuration. | Select Access & sign-in. |
| The page is replaced by 403 and Access Forbidden. | Your role holds neither permission above. | Ask a workspace administrator. |
Next
- Reading sign-in and access history - the record Verify Integrity checks.
- Reading your workspace activity - finding and opening a row.