Setting visibility scope
Visibility scope decides who can open an orchestrator and the documents under it. Every kind has the same Visibility Scope tab. It is meant for administrators, because it needs permission to read your organisation's roles, departments and groups.
- The IntELIEDocs app in your top bar.
- These permissions: Roles & Permissions · Role - List, Identity & Users · Department - List, Identity & Users · Group - List.
- Permission to update that kind of orchestrator. Without the directory permissions the tab still opens, but the switch is locked and a one-line note explains why.
If IntELIEDocs isn't in your top bar, your role can't view it or your plan doesn't include it. Ask a workspace administrator, or see Permissions and module visibility.
Steps
Open the tab
Open the orchestrator and select Visibility Scope in its tab list.
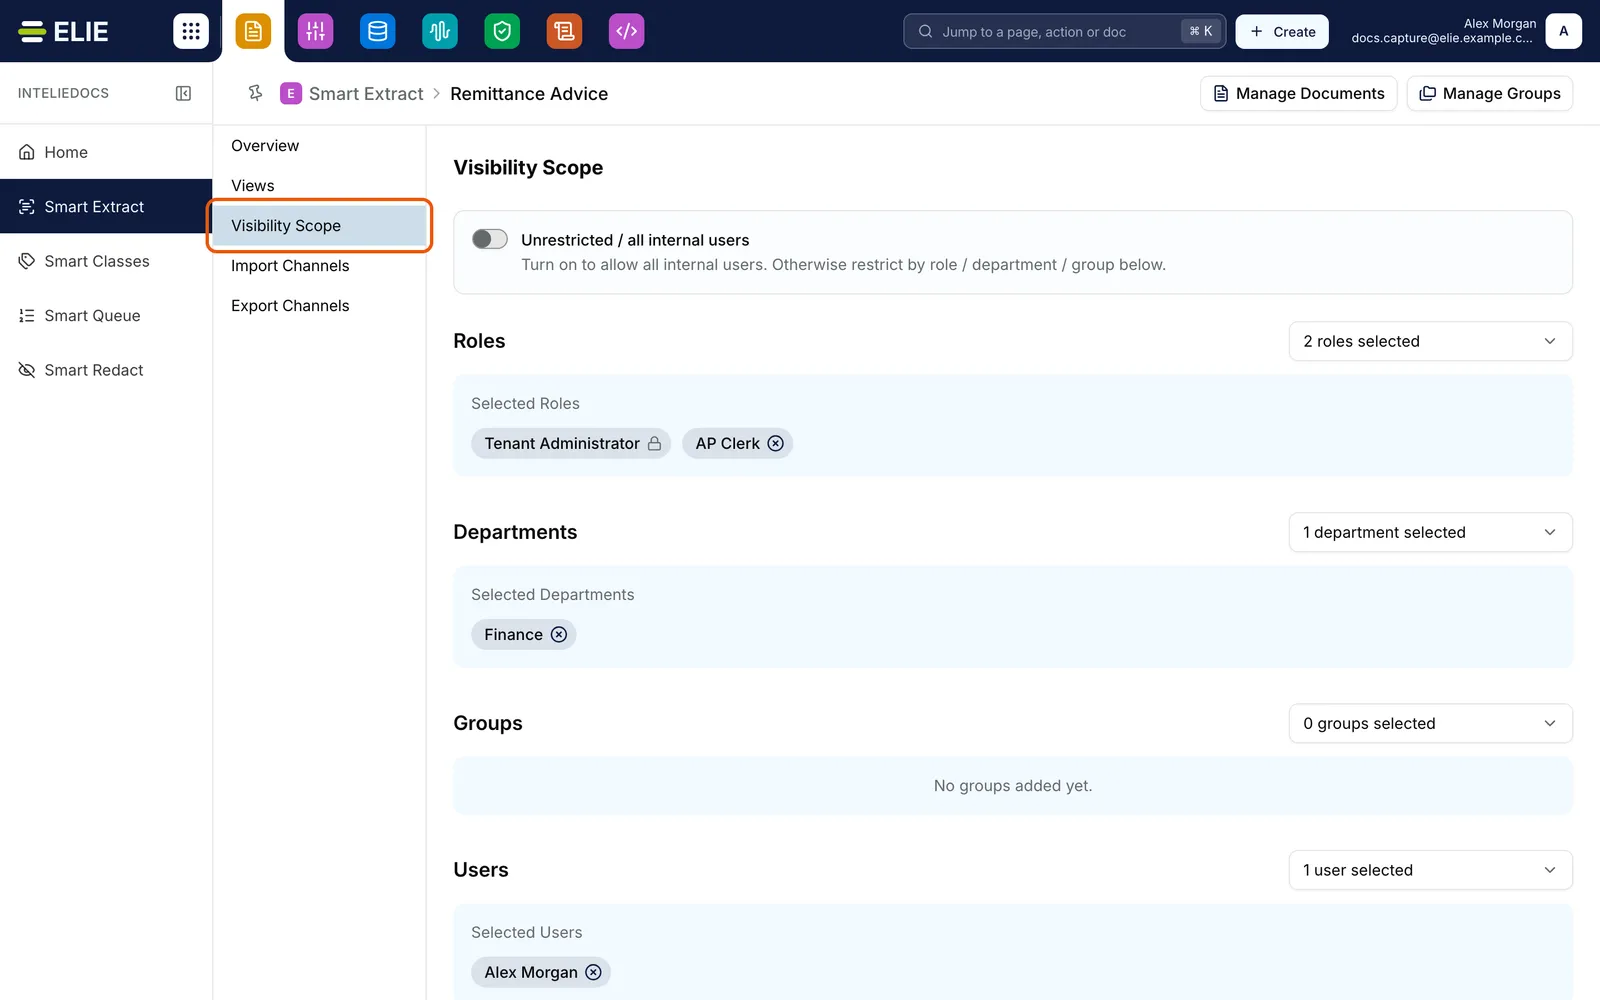
The Remittance Advice extract with the Visibility Scope tab ringed in its tab list. The scope is restricted: Tenant Administrator, locked with a padlock, and AP Clerk under Roles, Finance under Departments, no groups, and Alex Morgan under Users. EnlargeDecide how wide it should be
Leave Unrestricted / all internal users on for everyone in your tenant. Turn it off to restrict: the pickers appear, and your tenant administrator role is written into the scope straight away. Turning it back on empties every list.
Add the people who should see it
Work through the Roles, Departments, Groups and Users dropdowns, each with a Search by name filter. Ticked entries appear as chips below, under Selected Roles and its counterparts.
Remove a selection
Select the cross on a chip to take it out. Every tick and removal is written straight away, so there is no Save button.

What success looks like
- A confirmation appears for each change, for example Role added to visibility scope.
- Roles starts with your tenant administrator role, then lists exactly what you picked; an untouched panel reads, for example, No departments added yet.
Who is always in, and who can be added
Tenant administrators can open every orchestrator whatever its scope, so their role is pinned into Roles with a lock (Always has access) instead of a cross. Hover or focus the lock for "Tenant administrators always have access and cannot be removed from a visibility scope."
Users is not your full user directory: it offers only people whose role already grants view permission for that kind of orchestrator. Eligibility is per kind, so someone offered on a Smart Extract can be absent on a Smart Redact.
If something goes wrong
| Symptom | Likely cause | What to do |
|---|---|---|
| The switch is locked, reading "You do not have permission to view roles, so this cannot be changed. Ask a tenant administrator." | Your role cannot list roles. While roles are still loading it reads "Waiting for the roles directory. This cannot be changed until it loads." instead. | Ask an administrator to grant it. See Roles. |
| "You do not have access to Access Control" above the pickers. | Your role cannot read the Access Control directory, so the pickers have nothing to offer. | Ask an administrator to grant it. See Roles. |
| A colleague is missing from Users. | Their role does not grant view permission for this kind of orchestrator. | Give them a role that does, then reopen the tab. |
| Could not update visibility scope | The change was rejected and rolled back. | Reload the tab to see the real state, then try again. |
| An entry saved earlier has no chip. | It has since been deleted in Access Control or, in Users, the person no longer qualifies. A chip shows only for an entry the directory still returns. | Check it in Access Control, then add it, or its replacement, again. |
Next
- Import and export channels - feeding the orchestrator.
- Roles, Departments and Groups - where these pickers' entries are created.
- Smart Redact and Smart Queue originals - who sees an unredacted original is decided separately from this scope.